---
title: "Zero Trust Networking with Cloudflare WARP Client and Nodegrid SR"
slug: "zero-trust-with-cloudflare-warp-client-docker-version"
description: "Zero Trust Networking (ZTN) with Nodegrid SR family and Cloudflare WARP client protecting existing Branch and IoT equipment"
updated: 2023-04-13T12:23:14Z
published: 2023-04-13T12:23:14Z
canonical: "docs.zpesystems.com/zero-trust-with-cloudflare-warp-client-docker-version"
---
> ## Documentation Index
> Fetch the complete documentation index at: https://docs.zpesystems.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Zero Trust with Cloudflare WARP client (Docker Version)
## Cloudflare Zero Trust Usecase
ZPE as a Platform enables deployment of third-party services/applications such as [Cloudflare Zero Trust](https://www.cloudflare.com/products/zero-trust/) (the **Usecase**). This guide describes the main steps to deploy Cloudflare Zero Trust in a *ZPE Nodegrid Hive SR* as depicted in the following diagram.
> *Cloudflare Zero Trust replaces legacy security perimeters with a global edge, making the Internet faster and safer for teams around the world ...*.
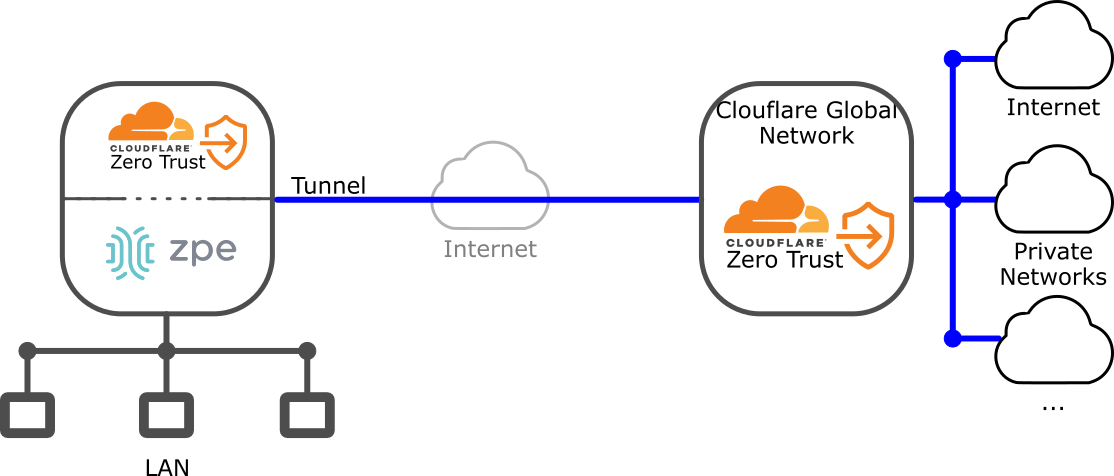
The objective of this usecase is to enable Internet traffic protection from and to a LAN deployed in a ZPE Nodegrid Hive SR by Cloudflare Zero Trust.
This guide structure is as follows:
1. Cloudflare Zero Trust environment configuration
2. ZPE as a platform: Deploying a third-party application/service
3. Validation of the scenario
## 1. Cloudflare Zero Trust environment configuration
The following guidelines are based on [Cloudflare Zero Trust Docs](https://developers.cloudflare.com/cloudflare-one/setup/).
### Prerequisites
- A Cloudflare account
### Start from the Cloudflare dashboard
1. On your Account Home in the [Cloudflare dashboard](https://dash.cloudflare.com/), click on the **Zero Trust** icon.
2. On the onboarding screen, choose a [team name](https://developers.cloudflare.com/cloudflare-one/glossary/#team-name).
3. To complete onboarding, select a subscription plan and enter payment details. This is still required, for the *Zero Trust Free plan*, but there is no charge.
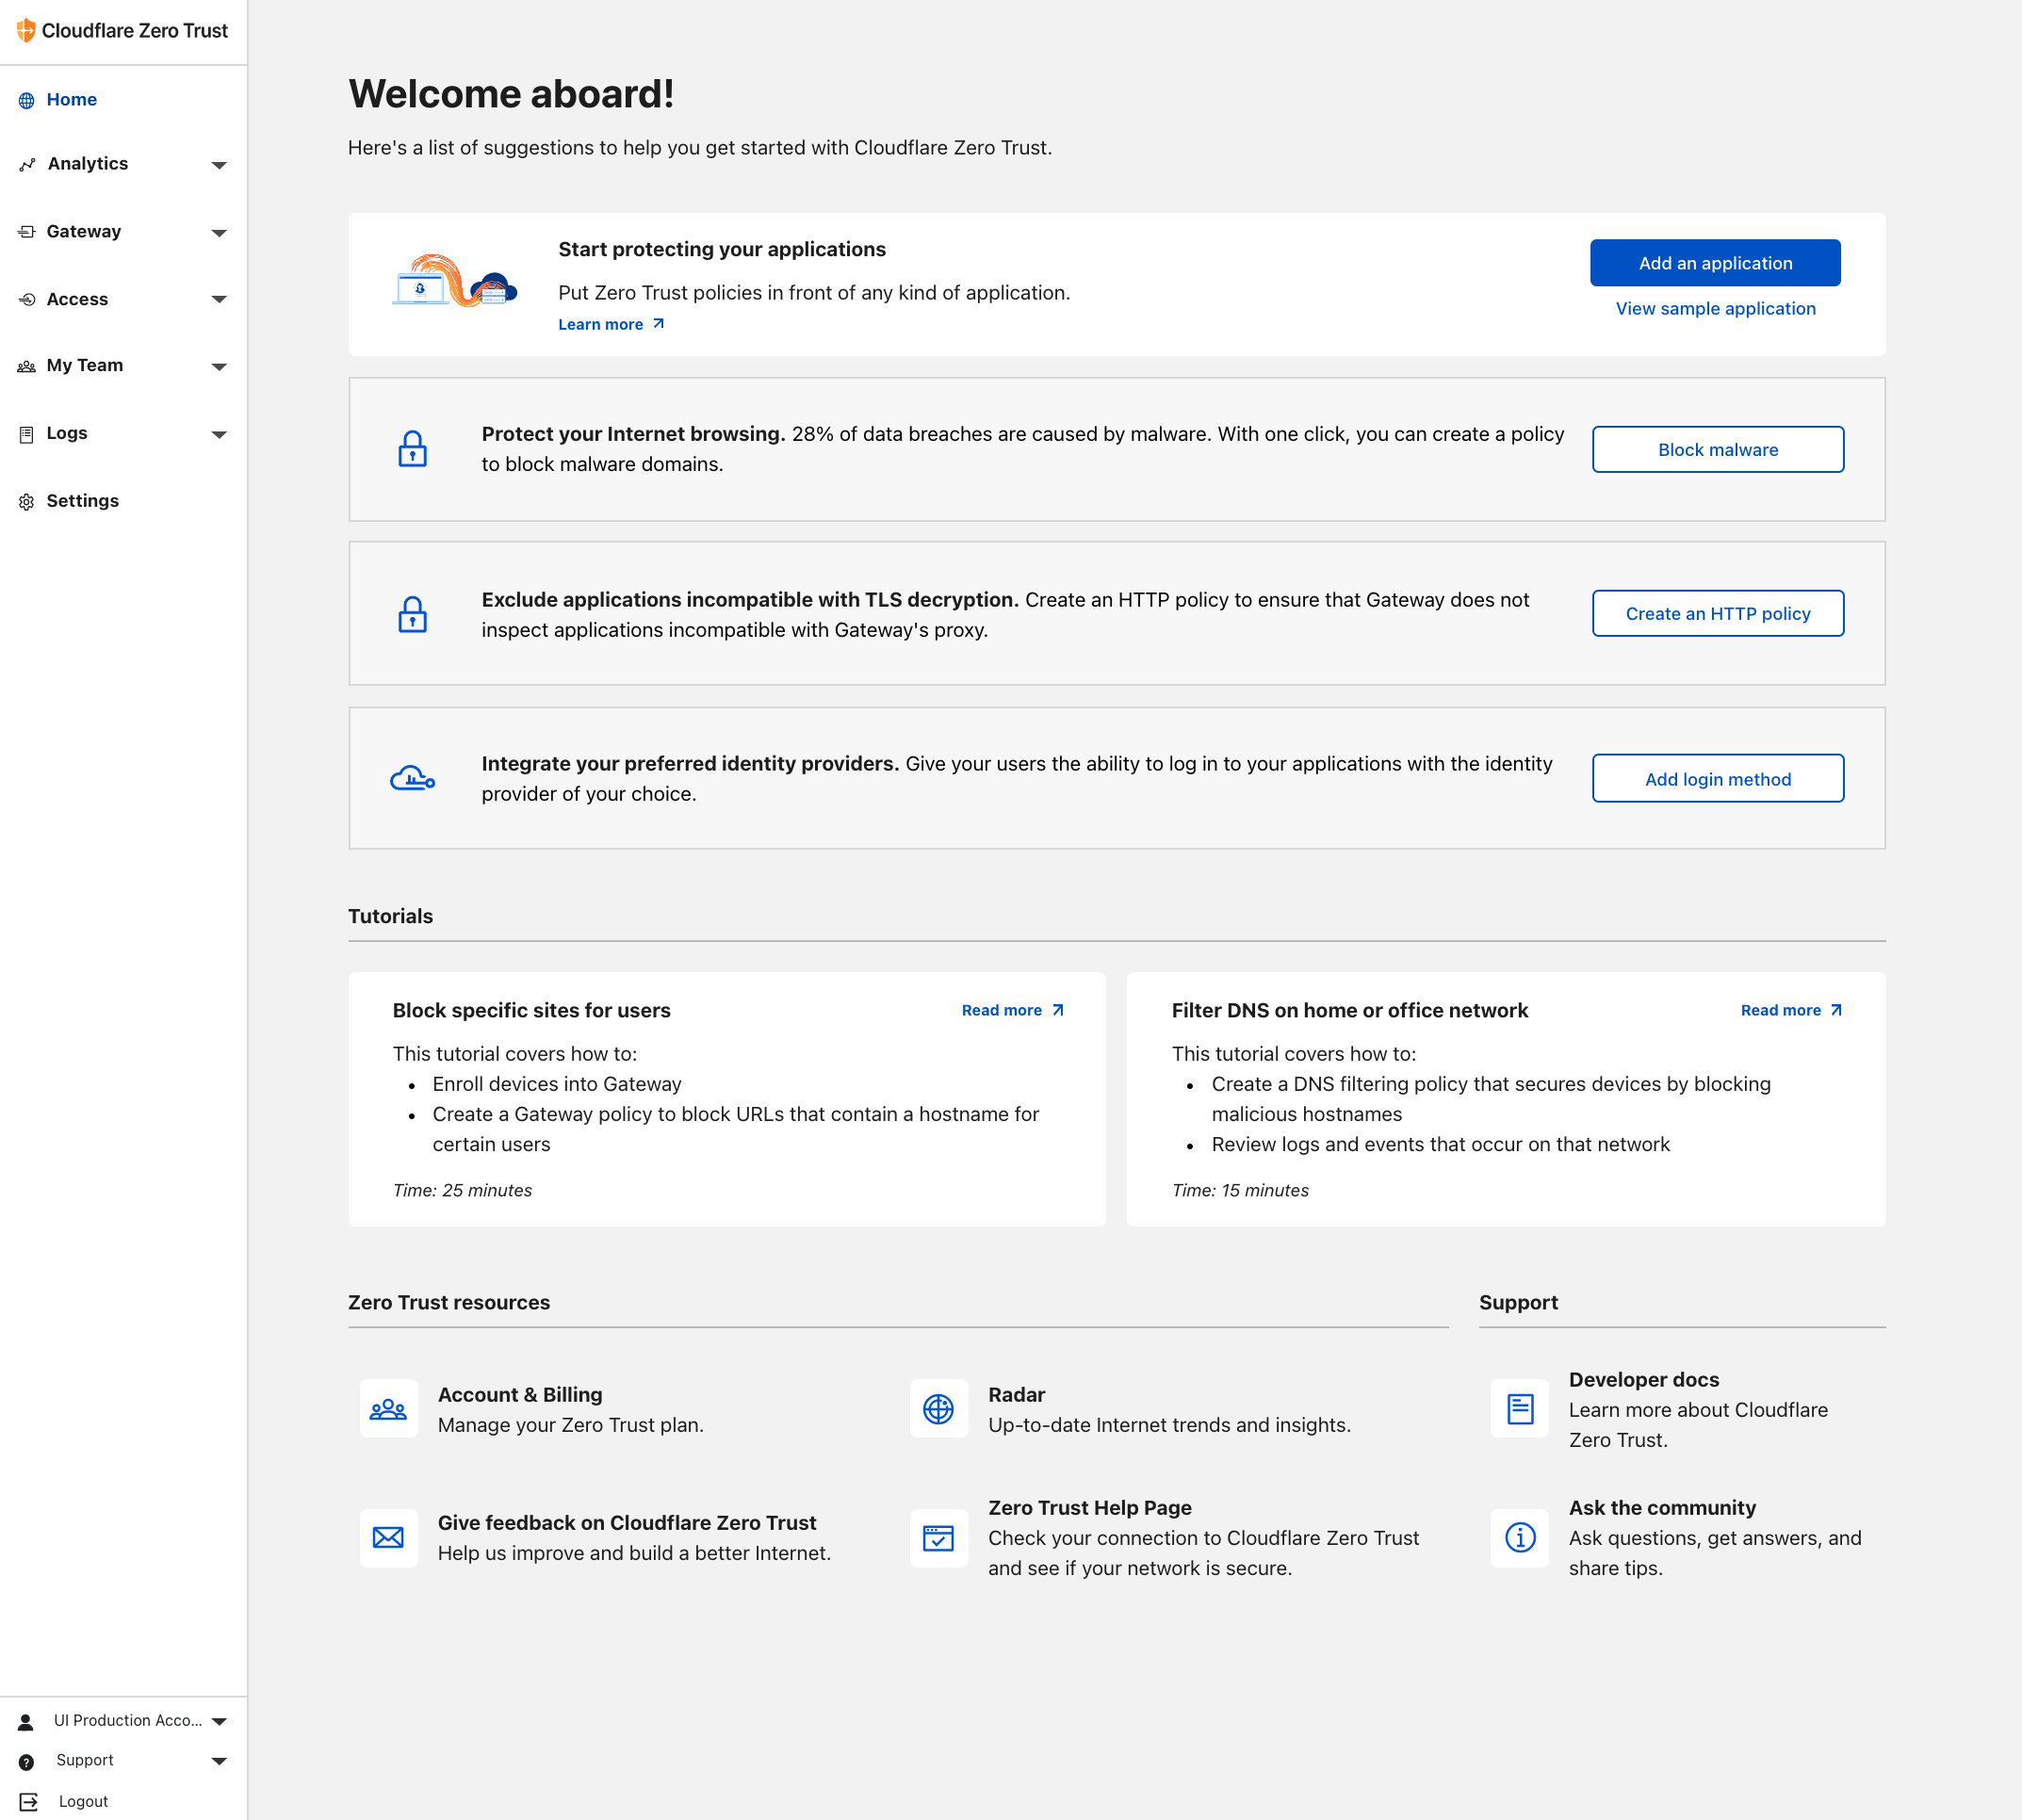
4. On the "Welcome to the Zero Trust dashboard!", explore the list of one-click actions (designed to help kickstart your experience with Cloudflare Zero Trust).
### Identity: [Service tokens](https://developers.cloudflare.com/cloudflare-one/identity/service-tokens/)
Cloudflare Zero Trust provides service tokens to authenticate against Zero Trust policies. *Cloudflare Access* generates service tokens that includes a *Client ID* and *Client Secret*. Automated systems or applications can use the tokens to reach an application protected by Access.
#### Create a service token
1. In the [Zero Trust dashboard](https://dash.teams.cloudflare.com/), navigate to **Access > Service Auth > Service Tokens**.
2. Click **Create Service Token**.
3. Enter **Name**. In the logs, this allows easy recognition of events related to the token. As needed, the token can be revoked individually.
4. Choose a **Service Token Duration** (token's expiration date).
5. Click **Generate token**. This displays the generated *Client ID* and *Client Secret* with request headers.
6. Copy the *Client Secret*.
> **Important**: This is the **only time** Cloudflare Access displays the *Client Secret*. If lost, a new service token must be generated.
The service token is used to configure Access policies and device enrollment rules.
### Set device enrollment permissions
This specifies users that enroll new devices.
1. In the [Zero Trust dashboard](https://dash.teams.cloudflare.com/), go to **Settings > WARP Client**.
2. In the **Device enrollment** card, click **Manage**.
3. In the **Rules** tab, click **Add a rule**.
4. Enter **Name**.
5. In **Rule action**, select **Service Auth**.
6. In *Include* subsection: **Selector > Service Token**, and **Value** > select the service token.
7. Click **Save**.
Go to **My Team > Devices** to review enrolled and revoked devices.
### Gateway Policies
Cloudflare Secure Web Gateway can set up policies to inspect DNS, Network, and HTTP traffic.
- **DNS policies** inspect DNS queries. Domains and IP addresses can be blocked from resolving on your devices.
- **Network policies** inspect individual TCP/UDP/GRE packets. Access to specific ports on the origin sever can be blocked, including non-HTTP resources.
- **HTTP policies** inspect HTTP requests. Specific URLs can be blocked from loading, not just the domain.
This guideline only considers the definition of a DNS policy to validate functionality, i.e., blocking a specific domain access from the LAN.
#### DNS policies
When a user makes a DNS request to Gateway, Gateway matches the request against the content or defined security categories. If the domain does not belong to any blocked categories, or matches an Override policy, the user’s client receives the DNS resolution and initiates an HTTP connection.
A DNS policy consists of an Action and a logical expression that determines the action's scope. To build an expression, choose a **Selector** and an **Operator**. In the **Value** field, enter a value or range of values. In this example, the policy blocks any domain that ends with `domain.com`.
1. In the [Zero Trust dashboard](https://dash.teams.cloudflare.com/), go to **Gateway > Firewall Policies**.
2. In the **DNS** card, click **Create a policy**
3. In the *Name your policy* section, enter **Name** and **Description** (optional).
4. In *Build an expression* section, for **Selector** enter **Domain**, For **Operator**, enter **matches regex**. For **Value**, enter `^*.domain.com`
5. In *Select an action* section, for **Action**, enter **Block**
6. Click **Save policy**.
### Set up Split Tunnels
This defines a LAN network to be excluded from WARP.
1. In the [Zero Trust dashboard](https://dash.teams.cloudflare.com/), go to **Settings > WARP Client.**
2. Under **Device settings**, select the *default* device profile and click **Configure.**
3. Under **Split Tunnels**, choose a Split Tunnel mode:
- **(default) Exclude IPs and domains** — All traffic is sent to Cloudflare Gateway except for the specified IPs and domains.
4. Click **Manage**
5. In the **Selector dropdown**, click **IP Address**.
6. Enter the IP address or CIDR, i.e., *192.168.99.0/24*
7. Enter Description (optional).
8. Click **Save destination**.
The *IP address* appears in the list of *Split Tunnel* entries. Traffic to these IP addresses are excluded from WARP.
### Deploy the WARP client in ZPE
This describes how to deploty the WARP client in ZPE as an Application, and the configuration of the LAN.
## 2. ZPE as a platform: Deploying a third-party application/service
This describes the deployment of a third-party application/service in a ZPE Nodegrid, specifically the Cloudflare WARP application. This configures Cloudflare Zero Trust to protect and police LAN traffic. There are two steps: a) deploy an application in a Nodegrid Hive SR, and b) Cloudflare WARP installation and configuration.
The application is deployed in a Virtual Machine (VM) hosted by a Nodegride Hive SR (see the following diagram):

### ZPE Requirements
This guideline is based on the following Nodegrid Hive SR:
| Field | Value |
| --- | --- |
| Version | v5.4.4 (Jan 29 2022 - 15:54:02) |
| CPU | Intel(R) Atom(TM) CPU C3558 @ 2.20GHz |
| CPU Cores | 4 |
| RAM | 15GB |
| Disk | 9GB |
| ZPE License | 5 VMs |
### Docker Containers deployment
The requirements for the Docker Containers are:
- 2 virtual network interfaces
- LAN access (*virt0 -> eth0*)
- WAN access (*virt1 -> eth1*)
#### Network configuration
On the Nodegrid Hive SR WebUI:
1. Go to **Network :: Connections**.
2. To create the **lan bridge**, click **Add**.
3. In **Name**, enter **brlan**.
4. On **Type** drop-down, select *Bridge*
5. In *IPv4 Mode* menu, select **No IPv4 Address** radio button.
6. On **Bridge Interfaces**, select **lan0**
7. Annotate the bridge name, e.g., `br0` (required).
8. Click **Save**
### ZPE application: Cloudflare WARP
Go to the Nodegride Hive SR console:
1. Access to the Console window
2. Clone the following repo:
```
git clone https://github.com/ZPESystems/cloudflare.git
cd cloudflare/docker
```
1. Edit the `warp/mdm.xml` file filling the required information in the `{field}` fields
Use the command
```
vi warp/mdm.xml
```
File content
```
organization
{organization}
auth_client_id
{auth_client_id}
auth_client_secret
{auth_client_secret}
```
> **NOTE**: All required details can be found in the Zero Trust dashboard from Cloudflare
>
>
> - The organisation name is the customizable portion of your team domain. You can view your team name in Cloudflare Zero Trust under Settings > General.
>
> team domain team name
| team domain | team name |
| --- | --- |
| .cloudflareaccess.com | your-team-name |
> auth_client_id and auth_client_secret are created during the step [Create a service token](/guides/docs/zero-trust-with-cloudflare-warp-client-docker-version#create-a-service-token)
1. Execute the bash script to install the Cloudflare WARP client
```
su
cd zpe-cloudflarewarp/docker
bash deployCloudflareWARP.sh --all --bridge br0
```
Proceed to the validation.
## 3. Validation of the scenario
The validation consists of:
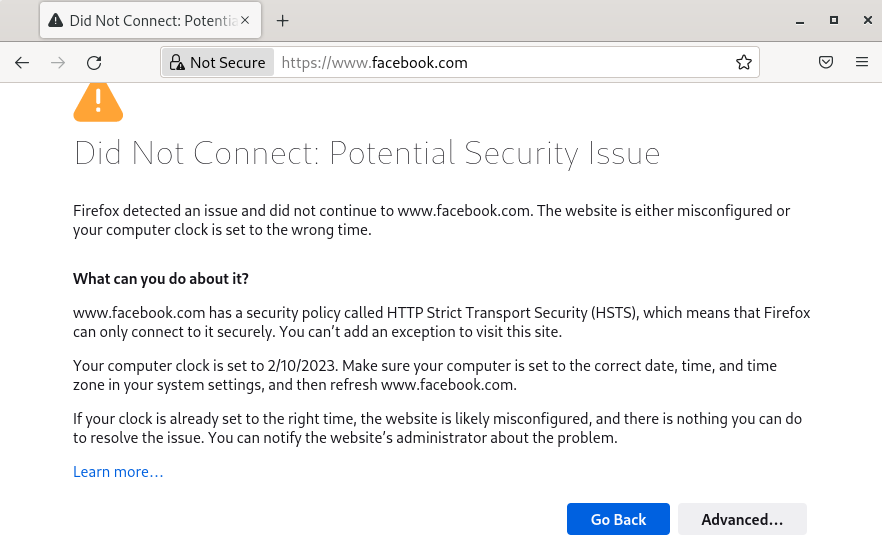
1. Define a firewall rule that blocks the following reg-exp domain in the [Cloudflare Zero Trust dashboard](https://dash.teams.cloudflare.com/)
- Reg-exp: `^*.facebook.com`
2. From a LAN Client go to the URL `facebook.com`
3. The Client should **not** be able to access the webpage
{height="" width="800px}